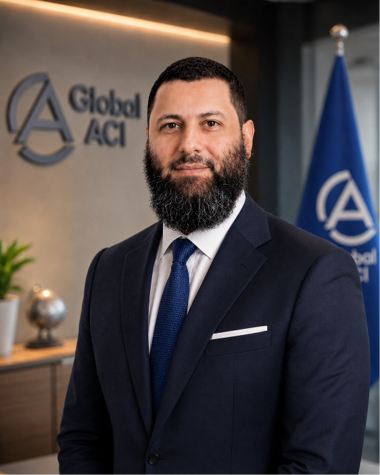
Dale Cyr
Inteleos
Dale serves as CEO and Executive Director of Inteleos, where he oversees healthcare certification programs with over 150,000 certificants in over 100 countries. With over 25 years’ of executive experience, he has pioneered initiatives that expand access to high-quality healthcare certifications worldwide.
Dale shares his expertise in business and certification through lectures and workshops around the world and is presently sits on the Board of Directors and is Chair of the Finance Committee for the American National Standards Institute (ANSI). and the Association of Talent Development (ATD) Credentialing Institute. He also is a co-inventor of a patent for a new type of test question and measurement.
Dale has his MBA in finance from the Albers School of Business and Economics, Seattle, WA, and has completed the Social Finance program from Oxford University, Oxford, UK and earned the Digital Transformation certificate from the Harvard Business School. Dale holds the Certified Association Executive (CAE) credential from the American Society of Association Executives (ASAE).
Laurie E. Locascio, PH.D. NAE
American National Standards Institute (ANSI)
Dr. Laurie E. Locascio began her tenure as president and chief executive officer of the American National Standards Institute (ANSI) in January 2025.
She previously served as Under Secretary of Commerce for Standards and Technology and director of the National Institute of Standards and Technology (NIST) following confirmation by the U.S. Senate in April 2022. In this capacity, Locascio oversaw NIST in its mission to promote U.S. innovation and competitiveness through measurement science, standards, and technology, including NIST’s implementation of the U.S. Government National Standards Strategy for Critical and Emerging Technology (USG NSSCET) and implementation of the CHIPS for America program at the Department of Commerce.
Prior to her appointment as NIST director, Locascio was vice president for research at the University of Maryland College Park and University of Maryland Baltimore, also serving as a professor of bioengineering. Before that, Locascio had a stellar career at NIST, rising from a research biomedical engineer to lead the agency’s Material Measurement Laboratory and finally acting as associate director for laboratory programs and principal deputy director.
Locascio is a fellow of the National Academy of Engineering, National Academy of Inventors, the American Association for the Advancement of Science, the American Chemical Society, and the American Institute for Medical and Biological Engineering.
She earned a B.S. in chemistry from James Madison University, an M.S. in bioengineering from the University of Utah, and a Ph.D. in toxicology from the University of Maryland Baltimore.
Marcus Long
IIOA (Independent International Organisation for Assurance)
Marcus was appointed IIOA Chief Executive in 2011.
Prior to joining IIOA Marcus was Head of External Affairs at BSI, building relationships with key international and national organizations.
Before BSI, Marcus worked in customer service and procurement in the rail, telecoms, retail and automotive sectors.
Marcus is also a member of the Global ACI Executive Committee as the Chair of the Stakeholder Committee.
Marcus chairs the BSI Suicide Prevention - Communications and engagement committee.
Warren Merkel
ANSI National Accreditation Board (ANAB)
Warren Merkel is the Interim Executive Director at ANAB.
Warren previously served as Vice President, Policy for the ANSI National Accreditation Board (ANAB), where he led ANAB’s public and international policy efforts. His responsibilities included engaging with stakeholders at the Federal, state and local levels and coordinating ANAB’s activities in international accreditation cooperations. Warren and his team also leveraged ANAB’s global engagement to support customers that operate in multiple markets.
Mr. Merkel serves as Vice-Chair of the Inter-American Accreditation Cooperation (IAAC) and Convenor of the ISO/CASCO Technical Interface Group. Previously, Mr. Merkel led the Standards Services group in the Standards Coordination Office of the National Institute of Standards and Technology (NIST). Mr. Merkel also co-convened the working groups that revised ISO/IEC 17025:2017, General requirements for the competence of testing and calibration laboratories and ISO/IEC 17060:2022, Conformity assessment—Code of good practice. Earlier in his NIST tenure, Mr. Merkel was Chief of the National Voluntary Laboratory Accreditation Program (NVLAP).
Brahim Houla
GCC Accreditation Center
Brahim Houla is Chair of Global Accreditation Cooperation Incorporated (Global ACI), Director of Accreditation Services at the GCC Accreditation Center, and Chair of the Asia Pacific Accreditation Cooperation’s MRA Council.
Brahim Houla is an Industrial Engineer with a DEA in Energetic Systems, including research studies in renewable energy.
He brings more than 25 years of experience in accreditation, conformity assessment and quality infrastructure at national, regional and international levels. He previously chaired the International Accreditation Forum’s Multilateral Recognition Arrangement Committee. His work focuses on strengthening international cooperation and recognition, supporting global trade, and ensuring that accreditation evolves to meet the challenges of digitalization, artificial intelligence and changing assurance needs.
Allyn Shultis
GRMA Allyn
As the Executive Director of the GRMA Allyn is charged with providing organizational leadership and management over the GRMA’s Programs. He also serves as an ex-officio member of all GRMA committees.
Previously, Allyn was the GRMA Board Treasurer and Technical Committee Co-Chair and was a featured representative among industry stakeholders which successfully helped launch the development process of the NSF/ANSI 455 Standards which worked to harmonized quality system requirements and best practices across various categories.
Allyn has decades of experience within Drug, Cosmetics, Medical Devices, and Consumer Product categories and has previously held a number of Quality, Operations, and Technical roles with Global responsibilities for First Quality, Covidien, and Tyco Healthcare.
Diana Kirsanova Phillips
SCS Global Services
Diana Kirsanova Phillips is Chief Assurance Officer and Chief of Staff at SCS Global Services, an international leader in third-party certification, validation, and verification across environmental, sustainability, food safety, and quality sectors. She has spent over 15 years working at the intersection of sustainability standards, accreditation, certification, validation, and verification. Her experience spans multiple industries, assurance frameworks, and certification and verification programs. This gives her a cross-scheme perspective on a problem familiar to conformity assessment bodies - translating standards, accreditation and scheme requirements into assurance systems that work consistently in practice. Her areas of focus include assurance governance, auditor competence, impartiality, quality, risk, and confidence in assurance outcomes.
In her current role, Diana provides enterprise-level leadership on assurance governance and works to strengthen the consistency and integrity of SCS Global Services’ assurance activities globally. Her work increasingly focuses on how assurance must evolve in response to emerging risks and technologies, including the responsible use of artificial intelligence in auditing while preserving professional judgment, impartiality, and confidence in certification outcomes.
R. Douglas Leonard
American National Standards Institute (ANSI)
R. Douglas Leonard Jr. is Chief of Strategic Initiatives at the American National Standards Institute (ANSI), where he works closely with ANSI leadership to advance strategic priorities related to standards, conformity assessment, emerging technologies, and U.S. competitiveness. Prior to this role, he served as Executive Director of the ANSI National Accreditation Board (ANAB), helping guide one of the world's leading accreditation bodies through a period of significant growth, diversification, and expanded impact.
With more than two decades of experience in accreditation, standards, and quality infrastructure, Doug is widely recognized as a leader in the conformity assessment community. Before joining ANAB, he served as President and Chief Operating Officer of the Laboratory Accreditation Bureau (L-A-B), where he helped expand internationally recognized accreditation services and strengthen confidence in testing, calibration, and inspection organizations.
Doug's leadership extends well beyond his organizational roles. He served as President of the National Cooperation for Laboratory Accreditation (NACLA), helping advance national and international recognition frameworks that support confidence in accredited laboratories and conformity assessment results. He has also served as a Lead Evaluator and Trainer for the Asia Pacific Accreditation Cooperation (APAC), conducting peer evaluations and helping develop accreditation professionals throughout the Asia-Pacific region. Through these roles, he has contributed to strengthening the global accreditation infrastructure that underpins trade, innovation, regulatory confidence, and market access.
Throughout his career, Doug has worked extensively with government agencies, industry leaders, standards developers, regulators, and international stakeholders to build trust in products, services, systems, and emerging technologies. He is known for his collaborative leadership style and his ability to bridge strategic vision with operational excellence, helping organizations navigate complex challenges while advancing innovation and public confidence.
Rich O'Brien
TIC Council Americas
Rich represents the testing, inspection, and certification sector to government and public stakeholders in the Americas. He previously led the Consumer Product Safety Commission’s international activities.
Rich is also a retired career U.S. Foreign Service Officer, and before joining the Foreign Service, he did trade promotion at the U.S. Commerce Department and earlier, at the Agriculture Department’s Foreign Agricultural Service.
Rich holds a master’s degree in International Affairs from George Washington University and a bachelor’s in Mass Communications from Towson University. A veteran of both the U.S. Air Force and U.S. Coast Guard Reserve, he has lived and worked in many places around the world.
Dr. Robert Slone
UL Solutions
Dr. Robert Slone is Chief Scientist and Innovation Officer at UL Solutions, where he is responsible for leading problem solving and innovation in safety, security and sustainability. Rob’s group includes UL Solutions Research & Development, Science Governance and the incubator teams for Artificial Intelligence and Modeling & Simulation.
With deep ties to the global scientific research community, he also serves as Executive Board Member of the International Science Reserve, a Venture Partner at Silicon Foundry, and is a board member of the Market Strategy Board of the International Electrotechnical Commission (IEC). Dr. Slone has been appointed as Affiliated Professor with the University of Notre Dame’s Lucy Family Institute for Data & Society and will focus his time on AI safety.
Dr. Slone holds a Bachelor’s in Chemistry with Honors from the University of North Carolina at Chapel Hill, an MBA with High Honors from The University of Chicago Booth School of Business (Wallman Scholar Award) and a Ph.D. in Inorganic Chemistry from Northwestern University (NSF Fellow). He holds 23 patents and was recognized as the Safer Choice Partner of the Year by the U.S. Environmental Protection Agency (EPA).
Kenny Cloft
Amazon
Kenny Cloft is a Senior Policy Expert at Amazon, where he develops and manages product safety and compliance policies that protect Amazon customers around the globe. He leads policy and compliance strategy for Amazon's Global from Day One initiative, which aims to let any seller list a product once and reach customers worldwide, with compliance guidance and testing built in at every step. His work focuses on consolidating country-specific testing, labeling, and packaging requirements into a single view, so sellers can test once and certify across multiple countries without re-testing for what has already been proven. He also supports work building AI-powered tools to modernize policy execution and customer protection. Prior to Amazon, Kenny worked in sustainable packaging development for consumer packaged goods companies and spent several years at NSF International leading global certification programs. Kenny brings deep regulatory and safety expertise to the future of global consumer protection.
Grace Burkard
ioXt Alliance
Grace Burkard, Director of Operations at ioXt Alliance, spearheads ioXt’s overall efforts in setting baseline security requirements to build a safer IoT world. Through her work with stakeholders and various international regulatory organizations, Grace plays a key role in harmonizing and standardizing security and privacy requirements, product compliance programs, and public transparency of those requirements and programs.
Jon Brandt
ISACA
Jon Brandt is senior director of professional practices and innovation in ISACA’s Content Development and Services department. In this role, he leads thought leadership initiatives relevant to ISACA constituents on audit, CMMI, GRC, emerging technology, information security, and privacy. He serves ISACA® departments as subject matter expert on infosec and leads innovative workforce readiness enablers. Brandt is a highly accomplished US Navy veteran with 30 years of experience spanning multidisciplinary security, cyberoperations and technical workforce development. Formal education includes an MSED in Workforce Education and Development from Southern Illinois University and BS in Cybersecurity from Champlain College.
Carl Bowman
CompTIA
Carl Bowman is a project manager at heart with a passion for the world of certification and all things IT. With over two decades of experience in the certification industry, Carl has in-depth knowledge of certification development processes, psychometric validity, ISO 17024 accreditation, creative approaches to exam delivery and global distribution, while embedding security into every step of the entire certification maintenance life cycle.
In 2005, CompTIA approved Carl’s proposal to bring all development initiatives inhouse and he now leads a team of sixteen staff, responsible for maintaining a
certification product portfolio that generates over $80M in annual sales for CompTIA. Fluent in both English and Spanish, he understands the challenges of managing a multilingual product portfolio and the validity concerns that come with translating high-stakes certification exams.
A strong believer in the value of technology, you will always find him researching and identifying ways to insert new software or hardware solutions into the operation to
improve processes and empower development teams to be more effective. In his spare time, you will likely find Carl hanging out with his family, hiking a mountain trail, playing classical guitar or jazz piano.
Brian Correia
SANS Institute
Brian Correia is the Director of Global Cyber Workforce Strategy & Engagement | GIAC Expert. He focuses on advancing the professionalization of the cybersecurity industry and driving the development of global workforce initiatives partnering with cyber leaders across government, major corporations, and national agencies that play a critical role in keeping communities safe, as well as with leading SANS experts actively working across every domain of the security field. As SANS | GIAC's leading workforce expert, Brian drives alignment across key global directives and frameworks including DoD 8140, NICE, and ENISA's ECSF and NIS2 while actively advancing cybersecurity professional designations with governments and agencies around the world.
Brian in his last job was the Managing Director of North America for (ISC)², which is another international cybersecurity leader in certification and membership association with over 150,000 members. These duties include enterprise/inside sales, events, and membership/industry advocacy within North America (USA & Canada) for this non-profit consortium best known for the CISSP certification.
Brian was formerly the Director of Business Development & Venue Planning for his current employer, the SANS Institute, and was involved in business development, sales, marketing, event management, and contracts. As an early employee of SANS, Brian built new products such as the onsite department, press room, cleared intelligence division, key processes to host numerous events throughout the year, and was the first account manager for large corporate and government clients.
Before working for SANS, Brian spent six years in the trade show industry working on the marketing, speaker bookings, and logistics for military, government, and corporate events. Brian also served three years on the Starwood Advisory Meetings Board helping to implement new products, marketing, and consulting to one of the leading hospitality companies in the industry.
Rick Gamache
ISC2
Rick Gamache is a cybersecurity executive and standards leader with nearly four decades of experience spanning government, military service, cyber threat intelligence analyst, consulting, and professional credentialing. A U.S. Coast Guard veteran, he has held senior roles in cybersecurity assurance, threat intelligence, governance, and professional standards, including serving as a Lead Cyber Auditor for the U.S. Navy.
Today, Rick serves as Senior Director of Standards & Practices at ISC2, where he leads work across professional standards, ethical practice, credential recognition, portfolio strategy, and research and analytics. His portfolio includes the evolution of the cybersecurity Common Body of Knowledge, the ISC2 Code of Professional Conduct, global workforce and competency framework alignment, and engagement with governments, regulators, academia, and industry.
Throughout his career, Rick has focused on the intersection of cybersecurity, professional competence, enterprise risk, and public trust. He is particularly interested in how cybersecurity matures from a technical discipline into a recognized profession with clearer standards of practice, ethical expectations, and accountability.
A systems thinker by nature, Rick brings a pragmatic perspective to emerging challenges including artificial intelligence, workforce development, cybersecurity governance, and the changing role of the security professional. His work is grounded in a simple principle: effective cybersecurity requires evidence, competence, and sound judgment, not just compliance.
Matt Isnor
Department of Defense Chief Information Office (DoD CIO)
Matt Isnor is a recognized leader in cyber workforce development with more than 20 years of experience leading enterprise-scale initiatives across the Cyberspace and Intelligence Communities. Currently serving as Chief of Cyber Workforce Development in the Department of Defense Chief Information Office (DoD CIO), he drives the standardization and advancement of the DoD cyber workforce through leadership of the DoD Cyberspace Workforce Framework (DCWF) and the 8140 Cyber Workforce Qualification Program. In this role, he helps align workforce capabilities with mission requirements, develops strategic workforce plans supporting the National Defense Strategy, and represents DoD workforce interests in partnerships with allies and international cyber stakeholders.
Before joining DoD CIO, Matt served as the Cyber Mission Force Program Lead for Workforce Development at U.S. Cyber Command, where he helped shape cyber training and certification standards across the Department of Defense and led workforce initiatives supporting critical cyber operations. His career also includes seven years of service in the U.S. Army, specializing in Signals Intelligence and operational deployments supporting national security missions. Matt holds an MBA in Information Systems from Hawaii Pacific University and a Master’s degree in Cybersecurity from Webster University.
Carolyn Sharkey
American Society for Clinical Pathology Board of Certification (ASCP BOC)
Carolyn Sharkey serves as Quality and Regulatory Analyst at the American Society for Clinical Pathology Board of Certification (ASCP BOC), the world's largest credentialing organization for laboratory professionals. She helps ensure the quality and integrity of the ASCP BOC's credentialing programs by leading Continuous Quality Improvement initiatives and supporting compliance with accreditation standards governing certification activities. Ms. Sharkey also collaborates on policy and advocacy efforts with ASCP BOC colleagues, leadership, and state regulatory agencies regarding licensure matters affecting credentialed laboratory personnel. Her work contributes to advancing professional standards, workforce development, and patient-centered laboratory practice by helping maintain the rigor, credibility, and recognition of professional credentials.
Her professional background also includes teaching science at the elementary and middle school levels and corporate customer care management. She holds an MPH with emphasis in Community Health Education from the University of Illinois Chicago.
Megan Smith-Branch
Leidos
Megan is an organizationally grounded AI enablement and governance leader who serves as a trusted advisor to C-suite and senior technology leaders, translating values and risk appetite into concrete operating models, policies, and behaviors. Megan combines industrial-organizational psychology, operational execution, and hands-on AI risk management to help executives set direction, orchestrate execution, and manage stakeholder alignment across complex, regulated environments. Megan’s current work focuses on operationalizing AI strategies with a human centric approach focused on cultural and behavioral change. Megan currently works as a Senior AI Enablement and Engagement Specialist at Leidos, is the former Deputy Director for AI Governance at Booz Allen Hamilton, former Chief Operating Officer at CertNexus and owner of Core Human AI.
Jim Wiggins
Federal IT Security Institute (FITSI)
Jim Wiggins brings more than 30 years of experience in education, information technology, and cybersecurity, including more than 25 years focused on information security and the past four years working extensively with artificial intelligence. His career spans cybersecurity, professional education, workforce development, certification, and emerging technologies.
As Chief Executive Officer of the Federal IT Security Institute (FITSI), Jim leads the organization’s role-based Federal IT Security Professional (FITSP) certification program. Under his leadership, the FITSP certification program achieved accreditation by the ANSI National Accreditation Board (ANAB) under ISO/IEC 17024, reinforcing its commitment to rigorous, independent, and internationally recognized personnel certification practices.
Jim holds a Master of Arts in Assessment, Testing, and Measurement in Education from The George Washington University and is a certified DACUM Facilitator through the DACUM International Training Center at The Ohio State University. He also holds the ICE Certified Credentialing Professional (ICE-CCP) credential and maintains numerous ANAB-accredited information technology and cybersecurity certifications.
His expertise increasingly focuses on the intersection of cybersecurity, artificial intelligence, professional credentialing, and workforce development. His AI-related credentials include the Artificial Intelligence Governance Professional (AIGP) and ISACA’s Advanced in AI Security Management (AAISM), Advanced in AI Auditing (AAIA), and Advanced in AI Risk (AAIR) credentials.